Trust Center
Your security posture, always current, always answerable.
 AnnexIQ Digital and AI Trust Platform
Know every AI system you run, and prove it is governed.
A registry, risk workflow, and policy library built for the way AI actually gets adopted inside a real organization, from the first project idea through to a governed system in production.
Know every AI system you run, and prove it is governed.
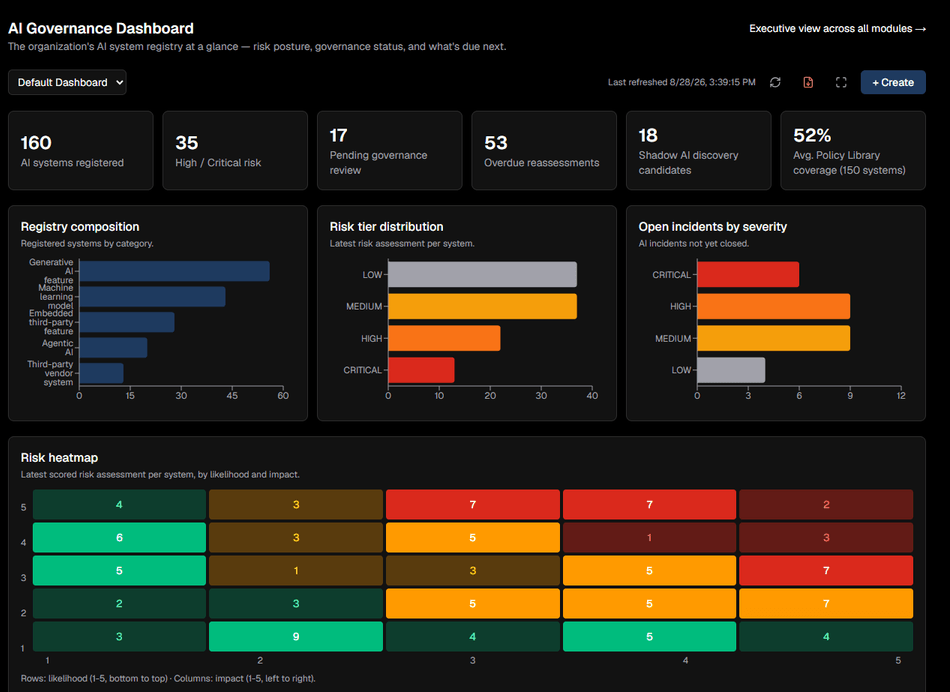
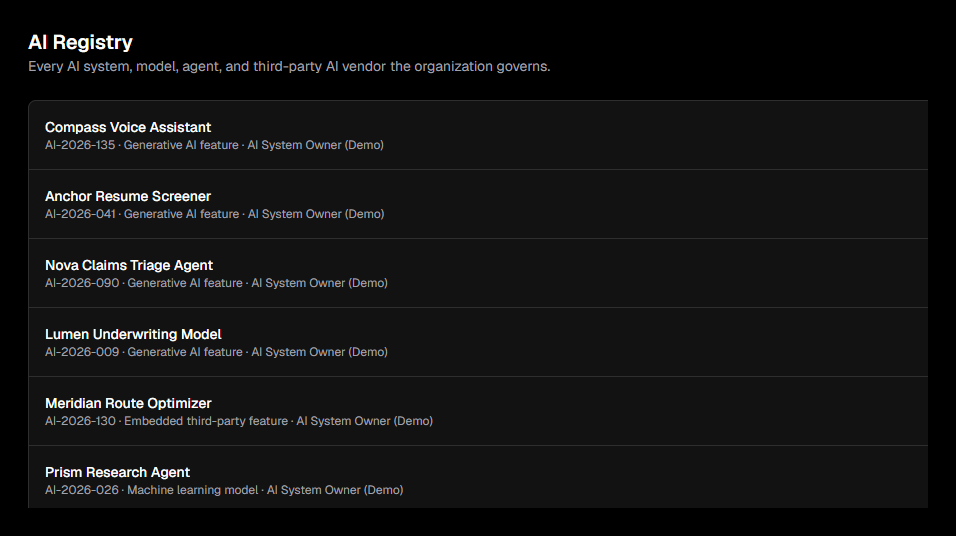
A living registry of every model, agent, and AI powered tool in use, with risk tier and governance status visible at a glance, so governance covers what's actually running, not just what was declared.
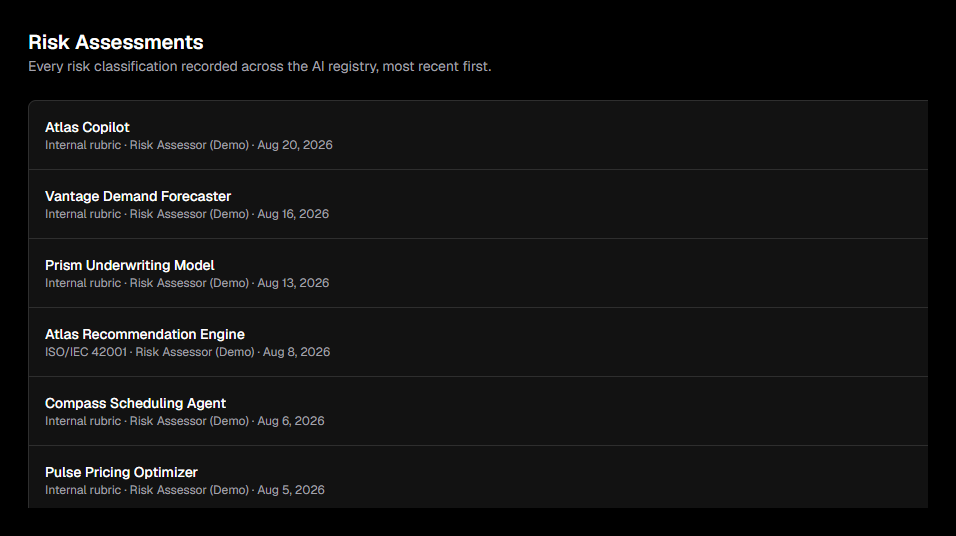
Every system carries its own risk assessment, logged against a real framework and a likelihood/impact rating, not a gut feel checkbox someone filled in once and forgot.
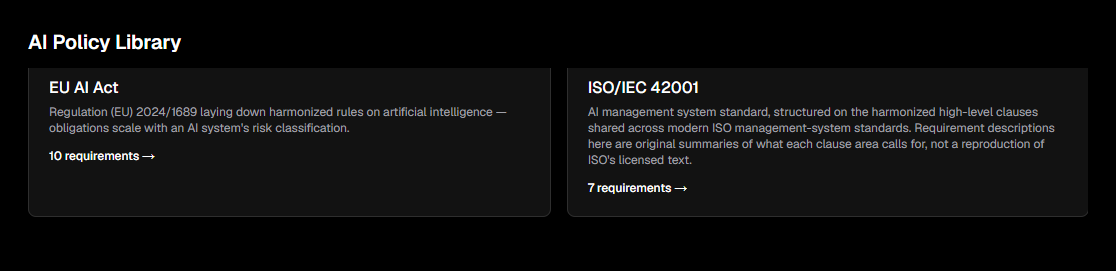
Maintain your AI policy and control framework in one place, EU AI Act, ISO/IEC 42001, NIST AI RMF, so an auditor or a regulator can see exactly which policy governs which model.
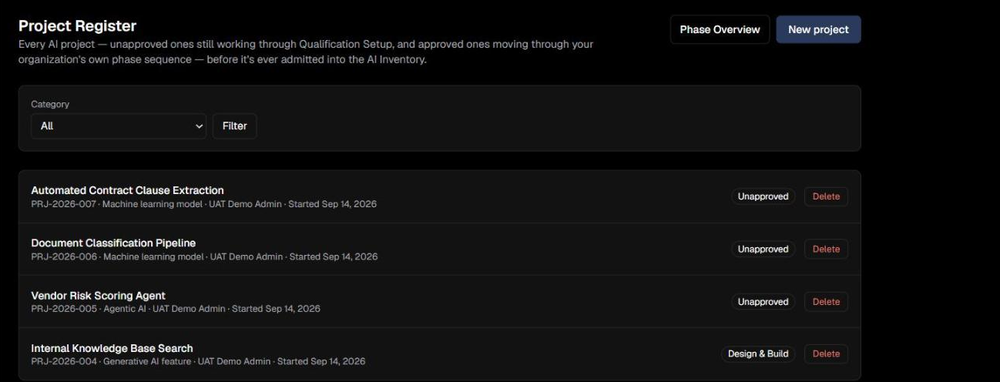
A demand is qualified against architecture, technical, and data checks, then approved into a phase template your organization defines, so a project only reaches the AI registry once it has actually earned the right to.
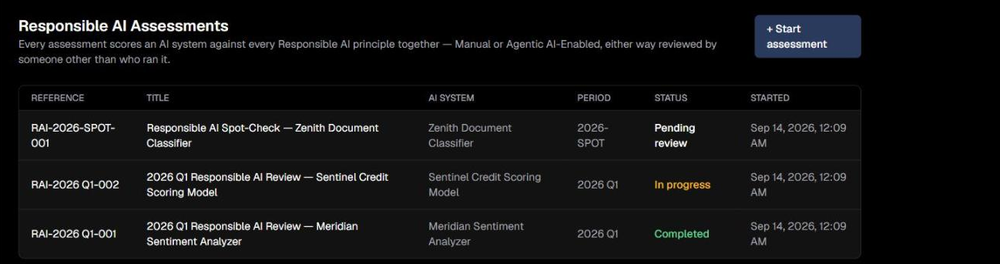
Fairness, transparency, accountability, safety, privacy, security, and sustainability, assessed manually or AI-enabled, always reviewed by someone other than whoever ran it, and always grounded in that system's own risk tier and red-team findings.
Your security posture, always current, always answerable.
Run your compliance program. Do not just document it.
Know what every AI system costs, and who owes for it.
Scan every model, red-team every agent, catch what leaves through a prompt.